Key takeaways:
- Cloud architecture layers front-end, back-end, storage, network, and security into one system. It is delivered through three service models (SaaS, PaaS, and IaaS) and deployed as public, private, hybrid, or multi-cloud.
- AWS, Microsoft Azure, and Google Cloud together account for nearly two-thirds of global cloud infrastructure spending, with AWS still the largest provider.
- Classic patterns like auto scaling, circuit breakers, and database sharding now sit alongside newer ones built for event-driven, serverless, and AI-heavy workloads.
- AI and machine learning workloads have added a new layer to cloud architecture decisions: GPU orchestration, model serving and routing, and FinOps-style cost governance.
- Zero Trust Architecture and DevSecOps have replaced perimeter-based security as the default baseline for new cloud architecture.
- Edge computing and sustainability (energy-efficient, carbon-aware design) are now standard inputs to cloud architecture decisions, not afterthoughts.
Cloud adoption and migration are now among the most important items on any corporate agenda, especially for companies wanting to harness digital transformation benefits as more and more workloads shift to the cloud, and more people work remotely.
Cloud architecture is the layered system of front-end interfaces, back-end infrastructure, storage, networking, and security that lets organizations deliver computing resources on demand over the internet. Global cloud computing revenue is projected to reach $1.04 trillion in 2026 and grow to $2.65 trillion by 2031, a 20.65% annual rate. For most companies, understanding this architecture underpins every other digital decision.
Companies now recognize the importance of cloud architectures, yet many still aren't sure what they entail, even as demand rises.
As forward-thinking business leaders continue to embrace the scalability, security, and malleability of the cloud, it’s crucial to understand what it means and where it's headed. This also means cloud providers have become essential allies for many companies.
In this article, we’ll explore cloud architectures, their key elements, available services and deployment models, and more.
Defining cloud computing architecture
Cloud computing is one of the most popular tech concepts right now. As a result, organizations are embracing virtualized services and resources on demand. Regardless of size, organizations now use cloud services to access or store information that's always available, from anywhere in the world via the Internet.
Cloud architecture is the design: the blueprint that defines which components a system uses, how they connect, and how they are secured and managed. Cloud infrastructure is what that design runs on: the physical and virtual servers, storage, and networking that providers operate. A well-designed architecture can run in private, public, and hybrid clouds and scale as demand grows.
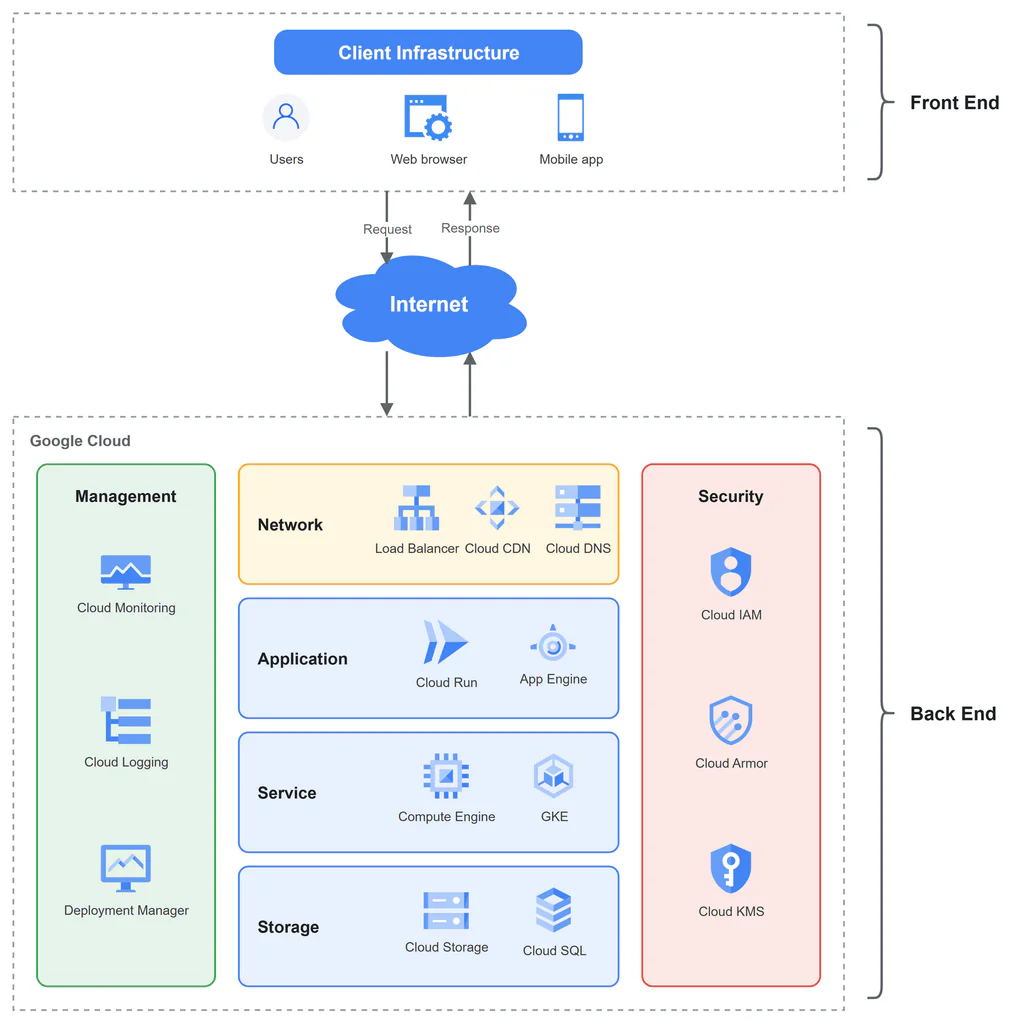
A traditional cloud framework includes service, network, security, and management layers, plus the back end and front end, which we'll discuss next.
- Cloud architecture: the design that combines front-end, back-end, storage, network, and security components into one cloud computing system.
- Cloud infrastructure: the physical and virtual servers, storage, and networking that a cloud architecture runs on.
- Front-end: the interface and applications users interact with to access cloud services.
- Back-end: the provider-managed infrastructure that stores, manages, and secures resources, including servers, storage, and virtual machines.
- Cloud-native application: software specifically built to run in a cloud environment, designed around patterns like auto scaling and distributed data handling.
- Hybrid cloud: an architecture that combines on-premises infrastructure with public or private cloud resources.
- Storage: A virtual place to manage and safeguard data.
- Management: Elements that help manage the application, service, runtime, storage, infrastructure, and other security mechanisms.
- Security: Practices and tools to employ diverse security mechanisms to keep cloud resources, systems, and files safe for end users.
- Network: An internet connection that bridges the front end and back end, allowing them to communicate.
Cloud architecture benefits
Organizations can almost completely remove their in-house hardware needs in terms of storage, servers, or networking elements such as routers thanks to cloud computing design.
The global cloud computing market crossed the trillion-dollar mark in 2026, and cloud infrastructure services spending reached $143.4 billion in the second quarter of 2026 alone, up 43% year over year, according to Synergy Research Group. That growth isn't evenly distributed: AWS holds 28% of global cloud infrastructure share, Microsoft Azure 20%, and Google Cloud 15%.
Frequently, companies adopt cloud models to host internal IT elements on an external platform. A major benefit is eliminating physical hardware like servers or data centers, as well as the costs that come with maintaining said hardware including facilities, electricity, cooling devices, and more.
Cloud architectures let companies move away from an upfront-cost mentality and shift toward an ongoing operating-expense approach. Cloud services are delivered through three main service models:
| Model | Who manages what | Best for | 2026 market share |
| SaaS (Software as a Service) | The provider manages the full application and the stack beneath it. The user configures settings and manages access and data. | Companies that want ready-to-use software without deployment overhead. | ~53% of cloud revenue in 2025, the largest segment |
| PaaS (Platform as a Service) | The provider manages the infrastructure, operating system, runtime, and middleware. The user manages the application and its data. | Teams build custom software on top of a managed platform. | Fastest-growing segment, projected at a 22.85% CAGR through 2031 |
| IaaS (Infrastructure as a Service) | The provider manages the physical hardware and the virtualization layer. The user manages the operating system, middleware, runtime, and applications. | Companies that want to pay only for the raw compute and storage they use. | Foundational compute and storage layer underneath SaaS and PaaS |
Figures above (SaaS share in 2025 and PaaS growth rate) are from Mordor Intelligence’s cloud computing market report.
What are the cloud deployment models?
Service models describe what the provider manages. Deployment models describe where the infrastructure runs and who shares it. An architect chooses both.
| Model | What it is | Best for |
|---|---|---|
| Public cloud | Infrastructure owned by a provider such as AWS, Azure, or Google Cloud and shared across customers | Variable workloads and teams that want fast provisioning without owning hardware |
| Private cloud | Dedicated infrastructure for one organization, on premises or hosted | Strict compliance, data residency, or latency requirements |
| Hybrid cloud | Public and private or on-premises environments connected and managed as one system | Companies with legacy systems, regulated data, or workloads that burst into the public cloud |
| Multi-cloud | Services from two or more public providers used together | Reducing dependence on one provider and using each provider’s strongest services |
Hybrid and multi-cloud are not mutually exclusive, and many enterprises run both.
A well-designed cloud architecture helps teams:
Release new apps faster
Update applications with cloud-native tools such as Kubernetes and speed up digital transformation
Simplify infrastructure management by relying on managed services
Scale data processing capacity as workloads grow
Strengthen security with provider-built controls, while the customer stays responsible for configuration, access, and data
Improve disaster recovery with backups and multi-region failover
Lower IT operating costs by paying only for the capacity in use
Support compliance by building on provider infrastructure that holds certifications such as ISO 27001 and SOC 2
Reduce breach risk with built-in encryption, monitoring, and access controls
Provision resources on demand
Scale applications up or down in real time with auto scaling
Meet availability and performance targets consistently
Cloud architectures offer many advantages. The most important ones include:
- Accelerate the release of new apps.
- Use cloud-native architecture like Kubernetes to update your apps and speed up your digital transformation.
- Simplifies the cloud system as a whole.
- Enhances data processing requirements.
- Offers superior security levels.
- Improved disaster recovery.
- Reduces the operational costs of IT.
- Ensure adherence to the latest guidelines.
- Prevent data breaches.
- Get resources quicker.
- Use hybrid cloud architecture to scale applications up or down, in real-time.
- Consistently meet service goals
Most cloud security failures trace back to customer-side misconfiguration, so these controls only help when they are set up correctly.
Cloud architecture patterns
A cloud-native application uses engineering practices that have worked well for some of the biggest and most popular websites in the world. Many of these practices aren't common, but the need for unprecedented scalability and efficiency drove their creation and adoption by the relatively small number of companies that really needed them. When a method is used enough times and works well, it becomes a pattern. A pattern is a repeatable way of doing something that produces the same result.
A cloud architecture pattern is a tried-and-true way to solve one or more problems in cloud-based applications. Cloud patterns are used in cloud-native apps. A cloud-native application is a program that was made to run in the cloud (AWS, Azure, private).
People don't always talk about design patterns for cloud-based apps, at least not until a company reaches a certain size. Even with so many design patterns to choose from, scaling when you need it is one of the hardest parts. Cloud architecture patterns are building blocks for cloud applications that can be assembled and managed on specific cloud platforms.
The table below compares 13 common cloud architecture patterns by the problem they solve, their main benefit, and where teams typically use them.
Top cloud architecture patterns compared
| Cloud pattern | Core purpose / problem solved | Key benefit | Typical use case |
|---|---|---|---|
| Auto Scaling | Automatically adjusts compute capacity based on real-time traffic demand. | Matches capacity to demand, controlling costs and reducing overload-related downtime. | High-traffic e-commerce during sales and streaming platforms. |
| Circuit Breaker | Stops requests to a failing service before it causes a cascading failure. | Increases system resilience and fault tolerance. | Microservices communication, payment gateway integrations. |
| Bulkhead | Isolates application components into independent pools or pods. | Ensures failure in one service doesn’t crash the entire app. | Multi-tenant SaaS applications, critical finance tools. |
| Database Sharding | Horizontally partitions large databases across multiple nodes. | Bypasses single-node storage and query performance limits. | Large-scale enterprise databases, social media platforms. |
| Event-Driven Architecture | Services communicate by publishing and reacting to events instead of calling each other directly. | Decouples services so they can scale, fail, and deploy independently. | Order processing pipelines, real-time analytics, IoT telemetry. |
| Serverless | Runs code in managed, stateless compute that scales to zero when idle. | Removes server management and bills only for actual execution time. | Image processing on upload, scheduled jobs, lightweight APIs. |
| CQRS (Command Query Responsibility Segregation) | Separates read and write operations into different data models. | Lets read and write scale and be optimized independently. | Best for complex business applications with a high read-to-write ratio. |
| Saga Pattern | Coordinates a sequence of local transactions across services, with compensating steps if one fails. | Keeps data consistent across microservices without a single distributed transaction. | Multi-step order or booking workflows spanning several services. |
| Sidecar Pattern | Deploys supporting functionality, such as logging or service mesh proxies, in a companion container next to the main service. | Adds cross-cutting capabilities without changing the main service’s code. | Service mesh observability, security policy enforcement in Kubernetes. |
| Gatekeeper | Uses a dedicated host as a broker that validates and cleans requests before they reach the application. | Shields services from malformed or malicious requests. | Public-facing APIs, regulated applications with strict input validation. |
| Retry | Transparently retries a failed operation that is likely to succeed on a later attempt. | Handles expected, temporary failures without user-visible errors. | Calls to external APIs or services, flaky network connections. |
| Throttling | Controls how many resources a single instance, tenant, or the whole service can consume. | Protects the system from being overwhelmed by any one consumer. | Multi-tenant platforms, public APIs with rate limits. |
| Valet Key | Issues a token that gives a client temporary, direct access to a specific resource. | Reduces load on the application by letting clients talk to storage directly. | Large file uploads and downloads, media streaming. |
Patterns like MapReduce and network-latency optimization (distributing users across edge locations) remain relevant for specific large-scale data and latency problems, but most new cloud-native systems are built from the patterns above.
AI, ML infrastructure, and FinOps in cloud architecture
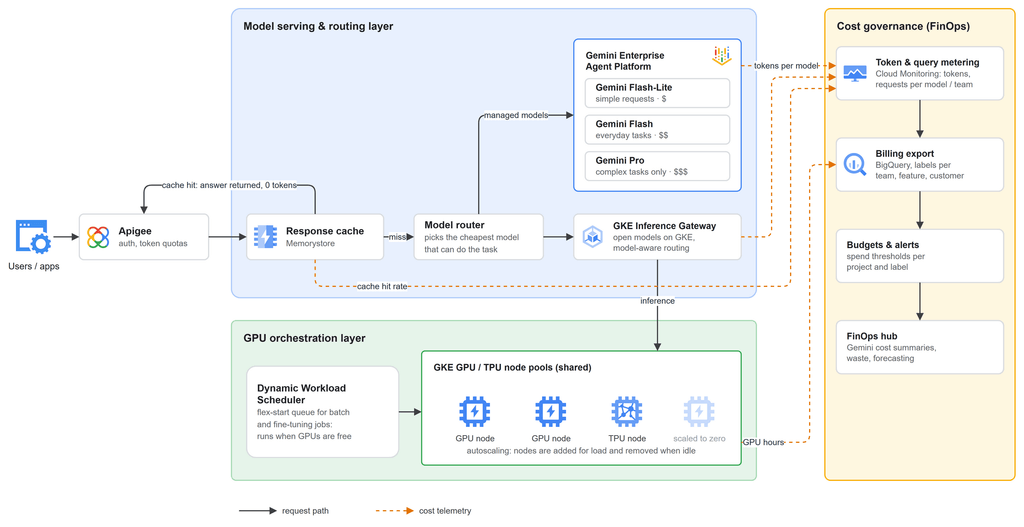
Cloud architecture in 2026 can no longer be separated from generative AI, large language models, and the GPU infrastructure that runs them. A typical AI-heavy architecture adds a layer most cloud-native applications never needed: a model-serving and routing layer that decides which model handles a request, a GPU orchestration layer that schedules compute across shared accelerators, and a cost-governance layer that tracks spend at the token and query level rather than server hours.
That last layer exists because AI workloads broke the old cost assumptions. Gartner forecasts that in 2026, spending on AI-optimized cloud infrastructure for inference ($23.3 billion) will overtake training ($19 billion) for the first time. Training is a cost architects can provision for once. Inference cost moves with every user request, which is why FinOps, the discipline of applying cost accountability and forecasting to cloud spend, has expanded specifically to cover AI workloads.
Architects now design for model routing (sending simple requests to smaller, cheaper models and reserving large models for tasks that need them), request caching to avoid paying twice for the same answer, and GPU scheduling that avoids paying for idle capacity.
Svitla’s guide to AI ROI and cost optimization goes deeper into sizing and governing this kind of spend.
Zero Trust Architecture and DevSecOps: the new security baseline
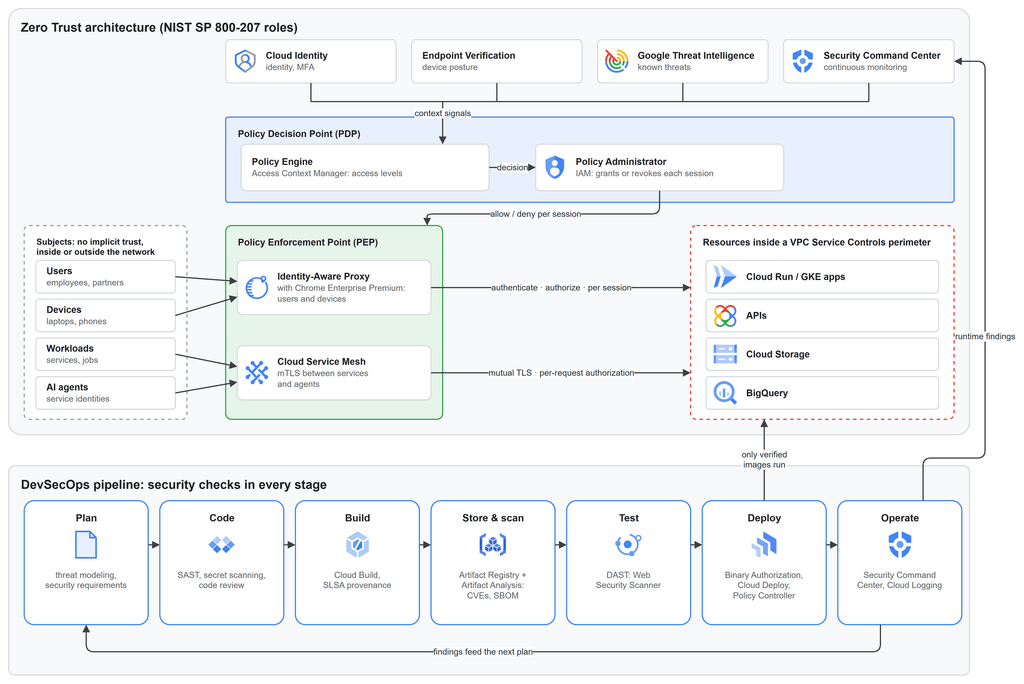
Cloud security architecture used to mean securing the perimeter: firewalls and VPNs that trusted anything already inside the network. That assumption no longer holds for distributed, cloud-native systems, so Zero Trust Architecture has become the default starting point for new designs.
NIST Special Publication 800-207 defines Zero Trust as a set of principles built around one core idea: no user, device, or service is trusted by default, regardless of whether it sits inside or outside the network. Every request is authenticated, authorized, and evaluated per session, and the enterprise continuously monitors the security posture of every involved asset, not just at login. Zero Trust works best when it starts from a clear view of where the risks are, so a cybersecurity risk assessment is a practical first step.
DevSecOps applies the same shift to the delivery pipeline, building security checks into every stage of development and deployment instead of reviewing security only before a release. Together, Zero Trust and DevSecOps make security part of the architecture itself.
Svitla’s practical guide to implementing Zero Trust Architecture walks through what that looks like step by step, and the team’s overview of agentic AI security risks covers the newer risks that come with AI agents acting inside that architecture.
Cloud architecture in practice: a Svitla example
The patterns above sound abstract until you apply them to a system under real constraints. Mueller Water Products needed to modernize an aging monolithic application built on .NET 2.0 and ASP.NET WebForms. Svitla’s team migrated it to AWS and split it into microservices, each with its own database, so one component could scale or fail without taking the rest of the system down. This isolation thinking is the same as the bulkhead pattern covered earlier in this article.
The results were concrete: page load speed improved tenfold, and support costs dropped substantially as the team moved off the legacy stack.
A second example shows the same ideas on Azure. A software company that sells an integrated risk management platform needed a cloud environment that could onboard clients in different regions. It also had to support workloads from production to low demand.
Svitla migrated the PHP and MySQL application to Microsoft Azure. The team used a hub-and-spoke network topology, Terraform for Infrastructure as Code, and Azure DevOps pipelines with Ansible to deploy repeatable environments. The client now runs ten environments, including production setups tailored to specific customers, and the partnership has continued for more than five years.
Edge computing: pushing architecture closer to the data
Not every workload belongs in a centralized cloud region. IoT sensors, connected vehicles, point-of-sale systems, and real-time industrial equipment generate data faster than it is practical to ship round-trip to a data center, and some use cases, like a factory safety system or a self-driving car, cannot tolerate that latency at all. Edge computing handles this by processing data closer to where it is generated, on local servers, gateways, or devices, rather than sending every byte to a centralized cloud region.
Worldwide spending on edge computing reached $265 billion in 2025 and is on pace to nearly double to $450 billion by 2029, according to IDC’s Worldwide Edge Spending Guide. In practice, this means architects increasingly design hybrid topologies: edge nodes handle time-sensitive filtering, aggregation, and inference locally, while the centralized cloud still handles heavier training, long-term storage, and cross-site analytics. The result is an architecture decision that changes where compute, security boundaries, and data governance each live.
Sustainability and green cloud computing
Cloud architecture decisions now carry an energy cost that is large enough to show up in global energy forecasts, not just a cloud bill. Data centers consumed roughly 415 TWh of electricity worldwide in 2024, about 1.5% of global electricity consumption, and the International Energy Agency’s Energy and AI report projects that figure to roughly double to around 945 TWh by 2030, driven largely by AI workloads. That growth is why sustainability sits alongside cost and performance as a first-class architecture concern rather than a separate initiative handled after the system is built.
In practice, this shows up as concrete design choices: right-sizing compute instead of over-provisioning for peak load, choosing regions with greener energy grids, scheduling flexible, non-urgent workloads to run when renewable energy supply is highest, and retiring idle resources instead of letting them run. AWS formalized this as the sustainability pillar of its Well-Architected Framework, treated as one of six pillars alongside security and cost optimization, which is a sign that cloud providers now expect architects to design for carbon impact the same way they design for the rest.
Cloud architecture examples
Many engineers choose Google Cloud as their go-to solution for cloud architecture because it is so flexible. The platform works well in many situations because it supports a wide range of application architectures. Google Cloud offers solutions for a wide range of use cases, including hybrid clouds, mobile apps, microservices, CI/CD, machine learning, and security, to name a few.
To illustrate, here’s an example of a hybrid and multi-cloud architecture:
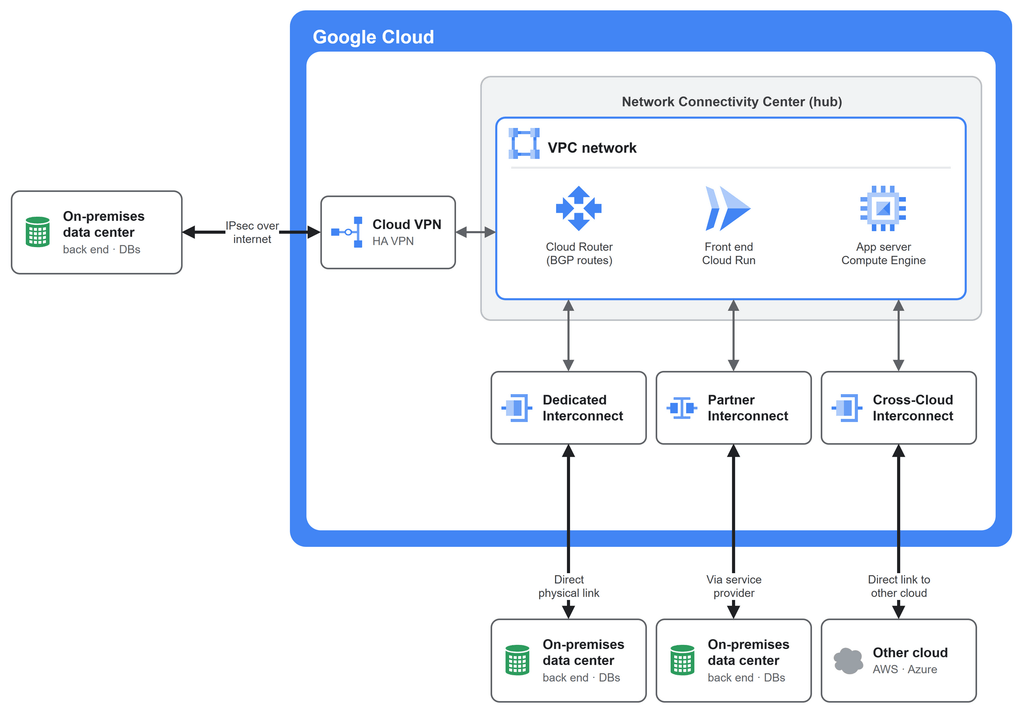
Hybrid architecture - Google Cloud
As this sample cloud architecture diagram shows, hybrid architectures are often used for migration or to run some applications on-premises and others in the cloud. The back end is hosted on-premises, while the front end and/or application server are hosted on Google Cloud. This is a common type of hybrid architecture.
Amazon
Amazon is a tech giant like no other. The AWS Well-Architected tool helps cloud architects build safe, intuitive, reliable, responsive, and effective infrastructure for a wide range of applications and workloads. AWS Well-Architected rests on six pillars: operational excellence, security, reliability, performance efficiency, cost optimization, and sustainability, giving customers and partners a consistent approach to evaluation and design as business needs evolve.
The AWS Well-Architected Framework includes domain-specific lenses, hands-on labs, and the AWS Well-Architected Tool. You can find the free AWS Well-Architected Tool in the AWS Management Console. It lets you review workloads regularly, identify high-risk issues, and track improvements over time.
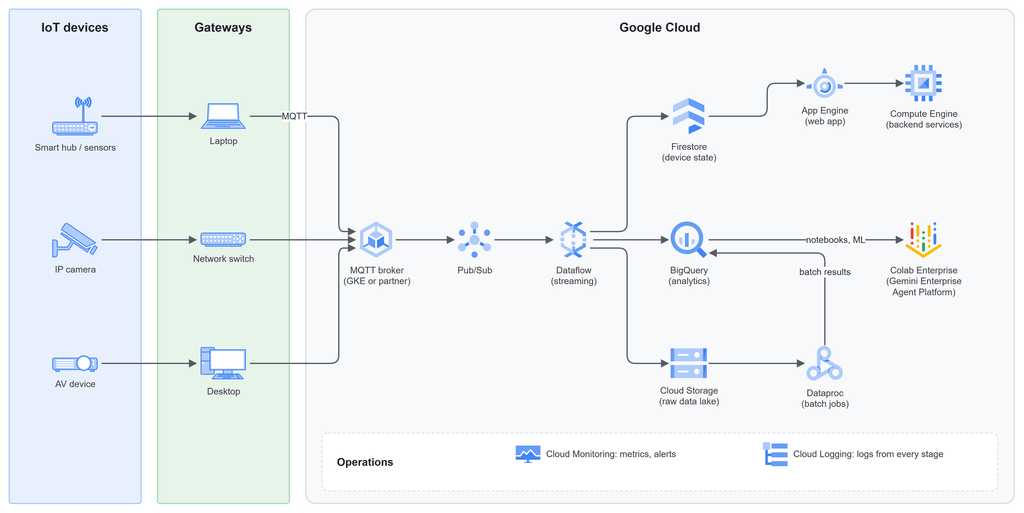
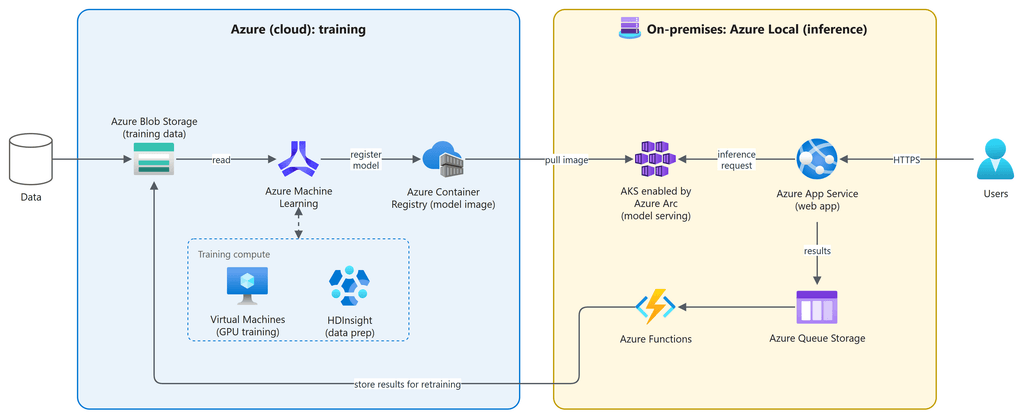
Cloud architecture diagrams
Using cloud architecture diagrams, a company can show how its enterprise cloud computing services are set up. A cloud architecture diagram can help you describe your company's cloud environment in documentation, change plans, or troubleshooting.
A cloud architecture diagram helps by showing how your system is built and how it works. Visuals can make complicated ideas easier to understand, and even non-tech-savvy people can better grasp a new idea through this communication method. Even though it's important to consider how cloud architecture diagrams can be used in general, you should also consider how they can be used in more specific ways.
Other key business reasons to use diagrams both for design and documentation purposes are:
- Document Current-State Infrastructure. With up-to-date documentation, companies can easily involve new employees or leaders and help them understand the infrastructure that supports their day-to-day work.
- How to Fix a Problem. A clear diagram can help you identify which parts might be causing trouble. Without a diagram, it can be hard to know which parts to look at first.
- Show that you're following the rules. If your business needs to maintain certain certifications, a diagram can help you organize your paperwork and show that you meet the required standards.
- Plan for Future States. When it comes to expanding or building on your organization's cloud computing resources, showing where you need to add parts or relationships can help you make the business case to your leadership team.
AWS offers multiple resources to create diagrams that describe the topology, deployment, and design of AWS products and resources built on its cloud platform. Here’s an example of a 3-tier architecture diagram:
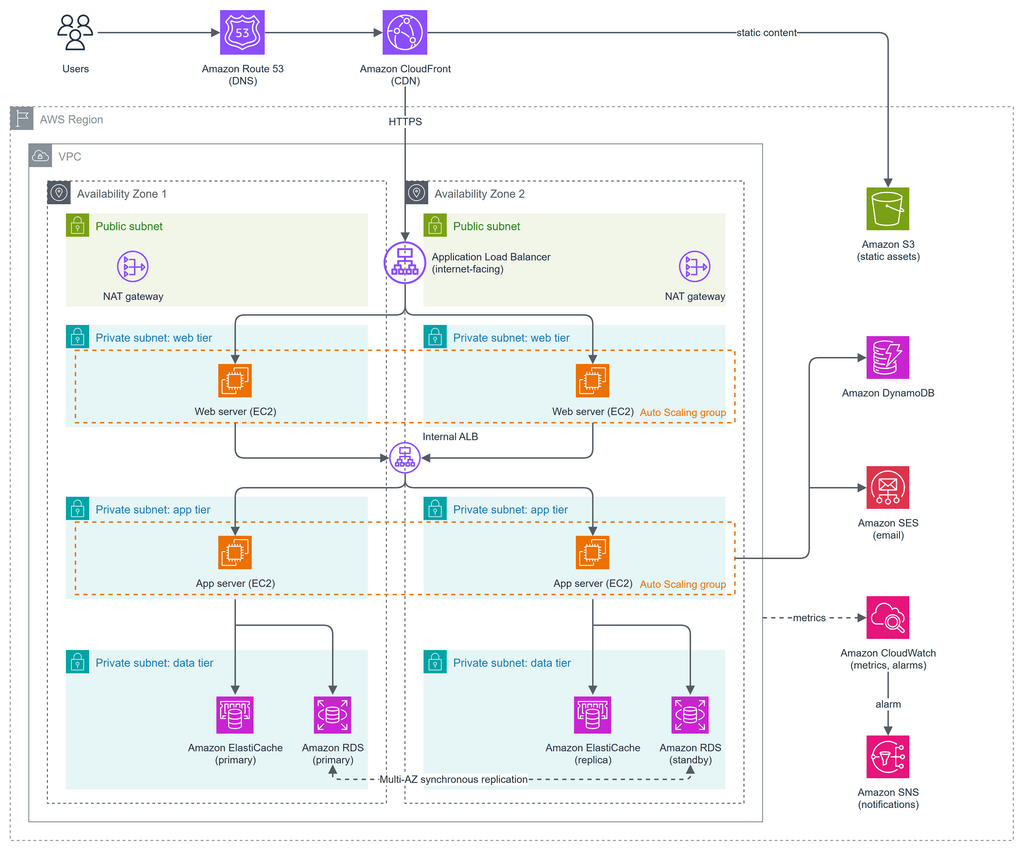
A 3-tier architecture separates the presentation, application, and data layers.
The Google Cloud Platform diagrams look like this:
And Microsoft Azure diagrams are similar to this:
More information to read (courses and certification)
If you’re interested in learning more about the fundamentals of web application architecture, we recommend reading this blog which is an all-in-one compilation of everything you need to understand about web application architecture.
To continue to learn more about cloud architecture, we recommend these helpful resources and cloud architecture tutorials:
- List of cloud architecture courses in Udemy
- Google Cloud Architect Certification
- How to Build a Rewarding Career With Cloud Architect Certification
- Preparing for Google Cloud Certification: Cloud Architect Professional Certificate
- Cloud Architect Masters Program
- IBM Courses for Cloud Architecture
- Professional Cloud Architect
- List of Cloud Architect Courses from Cloud Academy
- Udacity's "Become an AWS Cloud Architect" Course
- Cloud Architecture Patterns book
At Svitla Systems, we’ve worked on many cloud solution projects, helping clients adopt, implement, and accelerate digital transformation through cloud migration. To do this, we’ve tailored unique processes and team engagement models to ensure we address every aspect of cloud architecture and deliver successful outcomes.
If you’d like to learn more about how we can take your cloud architecture projects from zero to hero, reach out to our cloud experts who will be happy to provide all that you need.

FAQ
What is cloud architecture?
Cloud architecture is the combination of front-end interfaces, back-end infrastructure, storage, networking, and security layers that together deliver computing resources over the internet. It applies across private, public, and hybrid cloud deployments.
What's the difference between SaaS, PaaS, and IaaS?
The difference comes down to how much infrastructure the provider manages versus how much the user manages. SaaS hands over the full application, PaaS hands over the platform but leaves the application to the user, and IaaS hands over only the raw infrastructure.
What are cloud architecture patterns?
Cloud architecture patterns are proven, repeatable solutions to common problems in cloud-native applications, such as auto scaling for traffic spikes, circuit breakers for handling remote service failures, or database sharding for scaling beyond a single node.
Why do I need a cloud architecture diagram?
A diagram documents how your infrastructure is built and how components interact, which speeds up onboarding new team members, troubleshooting issues, demonstrating compliance, and planning future scaling.
Which cloud provider should I choose?
AWS, Azure, and Google Cloud together account for nearly two-thirds of global cloud infrastructure share, with AWS still the largest provider. Each offers a well-architected framework (tools, best-practice guidance, and lenses) to help you design secure, reliable systems. The right choice usually depends on your existing tech stack, team expertise, and specific workload requirements rather than market share alone.
What is the difference between cloud architecture and cloud engineering?
Cloud architecture is the design. It decides which services, patterns, and deployment models a system uses and how the layers fit together. Cloud engineering is the build-and-run work: engineers implement that design, automate the infrastructure, and keep it reliable and secure in production. Small teams often combine both roles, while larger organizations usually have architects set the blueprint and cloud engineers turn it into working infrastructure.
How do you design a multi-cloud strategy?
Start with the workloads, not the providers. Map which ones need a specific provider’s services, which must stay portable, and which carry data residency or regulatory limits. Then standardize what you can across providers, such as containers on Kubernetes, infrastructure as code with Terraform, and a single identity and monitoring layer. Set cost governance early, since each provider bills differently, and keep in mind that multi-cloud adds operational overhead, so it pays off mainly when resilience, regulation, or best-of-breed services justify it.